
Validate Your CUI Data Flow. Support Your SPRS Score. Prioritize Your Remediation.
KLC Consulting provides specialized CMMC Gap Assessments designed to validate defense contractor SPRS scores, shrink compliance boundaries, and deliver an actionable remediation roadmap. Combining authorized C3PAO insight with practical business operations experience, we evaluate your NIST SP 800-171 posture through cross-functional CUI data flow analysis. Our collaborative, non-punitive process honors your existing IT investments and establishes sensible compensating controls—giving leadership complete attestation confidence without disrupting active production.
The DoW’s 07/13 pause memorandum suspended the imminent requirement for independent C3PAO Level 2 certification assessments. However, the obligation to implement NIST SP 800-171 remains fully active under DFARS 252.204-7012, as it has since December 2017. Furthermore, defense contractors handling Controlled Unclassified Information (CUI) must perform a CMMC self assessment and submit their scores to the DoD’s Supplier Performance Risk System (SPRS) pursuant to DFARS 252.204-7019 and -7020. Contracting officers are required by DFARS 252.204-7024 to evaluate these SPRS scores when awarding contracts.
A KLC Consulting CMMC Gap Assessment helps defense contractors trace CUI data flows across all departments, evaluate NIST SP 800-171 implementation, calculate a defensible SPRS score, and establish an affordable remediation roadmap. Engaging KLC Consulting injects instant C3PAO credibility into your CMMC audit preparation. This third-party validation gives prime contractors and government contracting officers far greater confidence than a basic, unverified CMMC self assessment.
Why Conduct a CMMC Gap Assessment During the Phase II Pause?
On July 13, 2026, the Department of War suspended the transition to CMMC Phase II while the Reform Task Group conducts a review. The Department stated that Phase I self-assessment requirements remain in place and that NIST SP 800-171 Revision 2 compliance will continue to be enforced through self-assessment reviews and select government-led assessments during the review. For defense contractors handling Covered Defense Information, the immediate priorities are clear:
Ask Your Customer What They Require
Contact your contracting officer, prime contractor, or direct DoW customer. Requirements can vary by contract, solicitation, program, flow-down obligation, and customer cybersecurity expectations. Find out what they expect from you now rather than trying to interpret the CMMC pause in isolation. Many prime contractors are taking a “stay the course” approach and expecting their supply chain to maintain momentum.
Make Sure Your SPRS Score Is Supportable
If you are required to implement NIST SP 800-171, DFARS 252.204-7019 and 252.204-7020 require a current NIST SP 800-171 DoD Analysis for applicable covered systems, with the summary score maintained in SPRS. A score based on assumptions, old documentation, incomplete implementation, or a questionnaire that was never validated is risky. A KLC Consulting CMMC Gap Assessment establishes the technical and documentation baseline to support your score.
Now is the ideal time to push forward with your CMMC audit preparation and update your SPRS submission.
Why Third-Party Validation Matters During the CMMC Pause
Unverified Self-Attestation
- High risk of SPRS score overstatement
- Low assurance rating from Prime Contractors
- Vulnerable to DoW government spot checks and audits
KLC Consulting C3PAO-Backed Gap Assessment
- Instant credibility across the Defense Industrial Base (DIB)
- High-assurance standing for Prime Contractor inquiries and questionnaires
- Verified, defensible baseline prepared for government spot checks
Engaging an experienced C3PAO like KLC Consulting transforms a routine CMMC self assessment into a high-assurance posture that satisfies prime contractors and government auditors alike.
Key Priorities for Defense Contractors:
Maintain Contractual Compliance
DFARS 252.204-7012 mandates full NIST SP 800-171 implementation for handling Covered Defense Information.
Establish a Defensible SPRS Score
Unvalidated scores based on assumptions or outdated questionnaires create severe contractual exposure. A CMMC Gap Assessment ensures your published score is fully supported by concrete technical evidence.
Gain Prime Contractor Confidence
Tiered subcontractors must routinely respond to prime customer inquiries. Working with a C3PAO gives prime contractors significantly higher assurance than a DIY CMMC self assessment.
It Starts with a Business-First CUI Data Flow Analysis
Companies often view cybersecurity compliance as an IT concern. At KLC Consulting, our CMMC Gap Assessment begins by dispelling this myth. We start with a comprehensive, non-technical CUI Data Flow Assessment across your entire organization.
Our initial kick-off meeting brings together executive leaders and department heads across all operations, including Owners, Executive Management, Purchasing/Contracting, HR, Accounting, Compliance, Production/Manufacturing, Quality Control, Shipping, and IT.
This multi-departmental approach serves three essential purposes:
- Uncovers Hidden Exposure: Non-IT managers frequently discover that CUI exists in unexpected places (e.g., shipping logs, quality control records, or vendor quotes).
- Builds Executive Buy-In: Leadership gains a clear understanding of the project scope, realizing that cybersecurity is a core business priority, not just an IT task.
- Establishes Precise Scoping: Tracing CUI across people, processes, technology, facilities, and MSPs prevents over-scoping (which wastes money) or under-scoping (which causes assessment failure). Subsequent technical meetings then focus specifically on IT hardware, software, and operational technology (OT).
What the KLC Consulting CMMC Gap Assessment Evaluates
NIST SP 800-171 & 800-171A Objective Evaluation
We evaluate your System Security Plan (SSP) and supporting evidence against all 110 NIST SP 800-171 Revision 2 security requirements and their underlying 320 analysis objectives. We diagnostically test your NIST SP 800-171A security practices to determine what is implemented, what can be demonstrated, and what requires remediation.
DoW Methodological SPRS Scoring
Using the official Department of War scoring methodology (incorporating 5-point, 3-point, and 1-point deduction rules), we calculate your true SPRS score. Every point deduction is directly linked to a specific requirement and evidence gap. When requested, we also guide your authorized representative through the process of submitting or updating your score in SPRS.
A Collaborative C3PAO Approach (Not a Fault-Finding Mission)
Bringing in an outside consultant can cause natural apprehension among internal staff and IT teams. KLC Consulting operates with a collaborative brand ethos:
- We Build on What Works: We identify and highlight where your team is already doing a great job, building upon existing strengths rather than tearing down processes.
- Harmonized Recommendations: Drawing on deep business operations and consulting experience, we recommend security solutions that harmonize with fast, efficient production rather than creating operational bottlenecks.
- Zero Fault-Finding: We act as trusted advisors helping you prepare for future success, not inspectors looking for faults.
How the CMMC Gap Assessment Process Works
A structured 2 to 4 week engagement designed to deliver maximum clarity with minimal disruption to your daily operations.
STEP 1
Executive CUI Data Flow Analysis
Multi-departmental discovery interviews trace CUI across administrative, manufacturing, and technical workflows to establish your true operational baseline.
STEP 2
Boundary Scoping & Asset Categorization
We work with your IT staff and Managed Service Provider (MSP) to map network boundaries and categorize assets (CUI, Security Protection, Contractor Risk Managed, Specialized, and Out-of-Scope) according to CMMC Level 2 scoping rules.
STEP 3
NIST SP 800-171 & 800-171A Evaluation
We examine policies, system configurations, technical artifacts, and live demonstrations against all 320 assessment objectives to uncover evidence deficiencies.
STEP 4
SPRS Score Calculation & Prioritization
We calculate your recommended SPRS score and build a prioritized Plan of Action and Milestones (POA&M).
STEP 5
Executive Debrief & Business Roadmap
We present our findings in clear business terms to executive management, delivering an actionable plan that aligns cybersecurity with operational efficiency.
Remediation Strategy: Prioritize by ROI and Ease
KLC Consulting’s thorough CMMC Gap Assessment prevents premature and expensive technology purchases. Many compliance gaps can be resolved through configuration tweaks, policy updates, or operational adjustments without buying new software.
Our deliverable report provides clear, actionable guidance that prioritizes remediation based on three factors:
- Criticality & Risk Reduction
- Ease of Implementation
- Lowest Capital Cost
Our goal is to help you structure remediation so that your team achieves the fastest, most affordable increase in your SPRS score.
What You Receive at the Conclusion of Your CMMC Gap Assessment
- Complete CUI Data Flow Analysis & Boundary Diagrams
- Asset Categorization Schedule aligned with CMMC Level 2 scoping guidance
- NIST SP 800-171 & 800-171A Objective Gap Findings
- Official Recommended SPRS Score Calculation with supporting rationale
- Cost-Effective POA&M prioritized for rapid SPRS score improvement
- Shared Responsibility Matrix evaluation of your MSP and cloud vendors
- Executive Debrief Session translating technical findings into business decisions
- Expert Guidance for completing or updating your official SPRS submission
Note: These advisory deliverables do not constitute a formal government analysis or an official CMMC Certification Assessment. Under C3PAO ethics rules, KLC Consulting maintains strict separation between advisory consulting and official certification auditing.
Gap Assessment vs. Readiness Assessment
CMMC Gap Assessment is your meticulous mapmaker, pinpointing the exact gaps between your current security posture and CMMC requirements. This detailed assessment provides a roadmap with actionable recommendations, ensuring you prioritize the most critical vulnerabilities first.
CMMC Readiness Assessment is your final exam prep coach, simulating the actual audit and done by a C3PAO such as KLC Consulting. It gives you a clear picture of your overall preparedness. This assessment delivers a pass/fail or progress rating, providing you with the confidence and clarity to tackle the real test.
We’re a CMMC Consultant who provides Gap Assessment for DIB companies. Read transcript of our CMMC Gap Assessment Discussion Video.
Paul and Kyle talk about everything you need to know about in this CMMC Gap Assessment Video (a/k/a CMMC Readiness Assessment Video). And the difference between them and a CMMC Readiness Assessment.
[Paul] Good morning, Kyle how are you doing today?
[Kyle] good morning, Paul how are you?
[Paul] I’m well thanks. So, we’re going to talk today in this CMMC Gap Assessment Discussion Video about Gap Assessments, CMMC Gap Assessments. Which is a fairly popular service that we perform for clients. But we get a lot of questions about it. So, I thought it would be good if we talk and explain a little bit about that here in this video today.
[Kyle] yep absolutely.
What is a CMMC Gap Assessment?
[Paul] super so Kyle maybe just a quick overview, what is a CMMC Gap Assessment?
[Kyle] okay yeah Gap Assessment is an Assessment of where you are today based on CMMC level two. And most likely you’re going for the CMMC level two because that’s the one that requires a Gap Assessment. We’ll help you determine how many practices that you have implemented. Because at the end the end result is that you need to meet the CMMC level two controls which is based on NIST 800-171. So, we will help you identify how many controls you have, how many have implemented, and how many controls you need to implement. You know if you have partially implemented controls, we’ll document what else you need to do to complete the controls.
Gaps are areas of non-compliance
[Paul] so essentially those gaps if you will, are areas of non-compliance. Right with a particular control or with a particular assessment objective, is that correct?
[Kyle] that’s correct yep.
[Paul] okay and maybe this would be a good place in our CMMC Gap Assessment Video to talk about the difference let’s say between a Gap Assessment and a Readiness Assessment? So, they seem like they’re similar but maybe if you could explain what the difference is that would be helpful.
Difference between a CMMC Gap Assessment and a CMMC Readiness Assessment
[Kyle] yeah so, some people call it differently. In this CMMC Readiness Assessment Video we’ll call it Gap Assessment in the beginning. So, you know how much work it is going to take you to get to CMMC 2.0. A Readiness Assessment is something that we’ll do when you think you are pretty much ready for the actual Assessment. Then we will do a Readiness Assessment. These are the Assessments to see if you are truly ready for the final Assessment with the C3PAO, the Certified Third-Party Assessment Organization.
Right, they will hire a third party to do the Assessment on you. And they will do the Readiness Assessment. Readiness Assessment will consist of reviewing of your policies, procedures, and the system security plan the SSP. If you have any plan of action and milestones, the POAM, any gaps you still can get your CMMC certification right. But we’re going to review that as well, so these are the documentation we’re going to review. And also, we’re going to treat this like a mock Assessment.
Timing of a CMMC Gap Assessment versus a CMMC Readiness Assessment
[Paul] so it’s not clear to me, do people look to get a Gap Assessment early on in their process to figure out where they’re at with their compliance program? And a readiness Assessment later on when they think they’re ready? I think that would be helpful to know for our audience in this CMMC Readiness Assessment Video.
[Kyle] Yes, now you want to start as early as possible to get a Gap Assessment. Because you really want to know where you are so you can plan out your road map. If you have many practices that still need to be implemented, you can build yourself a road map. You want to do that as early as possible. And a Readiness Assessment is towards the end of your preparation. You want to get a readiness Assessment before the real Assessment.
How long does it take to do a CMMC Gap Assessment?
[Paul] okay that’s good to know. So, I think another helpful question to know in this CMMC Gap Assessment Video the answer to would be how long did they take? If a client were to come to us and say: yeah we’re interested in a Gap Assessment, a CMMC Gap Assessment (or CMMC Gap Assessment). What should they be expecting for the duration of that engagement for the Gap Assessment?
[Kyle] It really depends on the complexity of your IT environment. Also, the number of sites. How many sites do you have? Yeah so, some people have more physical sites, and you know multiple cage codes that will take a while. Um so if you have a fairly simple IT environment and uh it’s not too complex right. And only have one site, we can do it as quickly as one month or four weeks. But uh if it’s more complex obviously we’ll have to do an estimate.
[Paul] okay so that would be more on a case-by-case basis?
[Kyle] Exactly.
Can a CMMC Gap Assessment (or a CMMC Readiness Assessment) be done remotely, off-site?
[Paul] Now that that makes sense. What does the process look like maybe that would be helpful to know in this CMMC Gap Assessment Video? So, a client hires us to do a Gap Assessment a CMMC Gap Assessment. What does that process look like? Or the consultation look like? Do we need to go on site? Can we do them all remotely et cetera. Maybe you can just talk about that a little bit please for this CMMC Readiness Assessment Video
[Kyle] We can do this virtually. We don’t have to go on site unless there is a lot of physical security involved. And you know, then if we want to take a look at more on the physical security parts then we might go on site. But otherwise, virtual Assessment is what we normally do.
What’s the process for conducting a CMMC Gap Assessment?
[Paul] okay that’s good. So, Kyle what does the process look like for conducting a CMMC Gap Assessment or CMMC Readiness Assessment?
[Kyle] yeah, we will start with scheduling two or three Zoom calls to go through the process. If the process takes a bit longer, we’ll schedule more. But we will start with two or three zoom calls to go through the scope the practices uh that you have.
Client personnel who should participate in a CMMC Readiness Assessment
[Paul] okay good. And who needs to be present on these calls from the client perspective? Is it just the IT folks? Or who do you recommend?
[Kyle] initially as we go through the scope, I would say it’s better to involve all the people that touch CUI. And the department heads that have the people that touch CUI. Because IT may not know some of the business processes or the reason, some of the purpose of the processes from the other non-IT departments. So, it will be good for the business if some of the HR. If Purchasing and engineering get involved as well.
[Paul] Certainly because of, well especially with manufacturing, right? Manufacturers have all this operational technology. And IoT, internet things as well right. IIoT of things that also becomes or can become part of the scope of CUI, depending on their manufacturing processes, right?
[Kyle] yes right
CMMC Gap Assessment and CMMC Readiness Assessment begin with scoping CUI
[Paul] In terms of where we begin with this CMMC Gap Assessment Video Kyle, I think you talked about scoping CUI. And it seems like it’s pretty important to this process overall. Right to get the scope, right? So maybe we could just talk a little bit about that.
[Kyle] right, it is very important. As we are going through the Gap Assessment, we want to make sure that the company has the right scope. And the company might already define the scope. But we will verify the scope. And we will walk through the data flow and the data life cycle for the CUI. All right so we’ll go through the CUI.
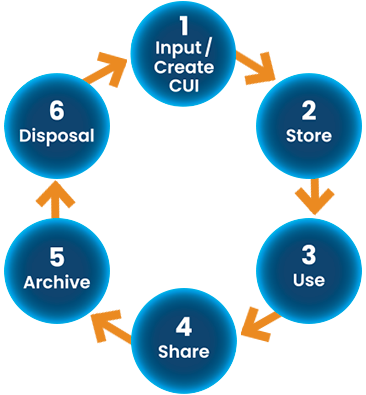
KLC scopes CUI using our proprietary CUI Data Lifecycle approach
How does the CUI get into the company’s environment? The input and creation. Then we’ll go through the storage of the CUI. Where it’s stored. Who actually manages the storage? And how it’s actually stored. The usage: the people, processes, and technology. Applications that touch CUI. Sharing of CUI, the vendors, the subcontractors, the prime contractors. How do you share that CUI? Who do you share with? And also, the archiving and the backup of the CUI. Where is it stored? How do you do the backup? And also, at the end of the lifecycle, the last step is how these destroy that data right how do you destroy it and then who’s actually responsible for destroying? Do you outsource it?
So, once we go through that life cycle we will verify to see if you have the right scope that’s where we start and if the scope is a little bit different from the company has defined previously, we will adjust and make sure that company have the right scope.
Commercial Off The Shelf COTS Exemption
[Paul] right okay now that’s good to know for this CMMC Gap Assessment Video. So, we begin with scope you get the scope. Well first of all, I guess we should back up and say: We determine that it’s not COTS. Because that’s part of this process as well. But assuming that this particular client is not a COTS vendor and doesn’t qualify for a COTS exemption. We go through the CUI data lifecycle. And scope CUI first when we do a CMMC Readiness Assessment.
What comes next then? So how do you, how do we then go and proceed after we have the scope clearly defined?
We distinguish CUI and non-CUI assets during a CMMC Gap Assessment
[Kyle] right so once we go through the scope the data lifecycle, one of the reasons is to define the systems and the applications that are in scope. Right the assets that are in scope. So, once we understand these assets, the CUI assets, and the security protection assets, like the firewall, VPN, what kind of security technologies they have? Then we will be able to more clearly, more precisely ask the right questions. How the practices apply to these types of assets. So, we will be able to walk through the practices. We’ll go through each one of them based on the assets that are in scope. So, we don’t have to talk about all the assets that not in scope. And we will go through for example, Access Control. How do you access the assets that are in scope?
Cloud Services and CMMC Gap Assessment
[Paul] okay and so with some of our clients who come to us, they use cloud services. How do cloud services affect or impact a CMMC Gap Assessment?
[Kyle] yeah so as we go through the Gap Assessment, we’re going to define the asset inventory right. We’re going to go through your CUI assets. And identify and list out your assets that are on-prem, and also in the cloud. So, if you have multiple environments, we’re going to take that into consideration. And there are going to be some checks. If you are using cloud, we might look for some Fed Ramp certification for example right. So, there are certain criteria when you are using a third party, the cloud services, we’re going to do some verification on some of the requirements. Some of the cybersecurity requirements: the encryption and requirements right that should be applied to some of these vendors.
MSP services and CMMC Gap Assessment
[Paul] okay so Kyle we talked a little bit about the cloud what about client company MSPs in this CMMC Readiness Assessment Video. How does that factor into the Gap Assessment or the overall compliance program?
[Kyle] If your IT is outsourced to some of the managed service providers, then during the interview we will need to have them involved. Because they are more familiar with your IT in terms of some of the configurations. Specific configuration questions, change management, how they manage some of the network security parameters. Security, even the cloud if they manage the cloud for you. They will have the answer so we will need them to get involved during the interview process.
Factors that affect the cost of CMMC Gap Assessment
[Paul] okay now I know we a little bit earlier in this CMMC Readiness Assessment Video, we talked about um you know complexity affecting the cost. And the time duration of a CMMC Gap Assessment. But what are some of the other factors there if we were to just elaborate a little bit about those? Let’s spell those out, what would be the factors that would impact both the duration and the cost of a Gap Assessment?
[Kyle] The number of systems involved could be many different directions.
[Paul] okay yeah okay. Kyle some clients are using SaaS, software as a service. Some use cloud service providers. How does that impact the Gap Assessment? Or really their overall compliance program with NIST 800-171 and CMMC?
Cloud services, shared responsibility matrix, and CMMC Gap Assessment
[Kyle] Right, so the cloud service providers, we will look into the shared responsibility matrix. Most likely you will need to request a copy if you don’t already have one. And during our Gap Assessment we are going to identify what responsibility belongs to the cloud service provider. Or the third-party service that you use. And what responsibilities belong to you. Some of them are going to be shared right. They’re going to be some portion taken care by the service provider, and some by you right.
We’ll go through the Shared Responsibility Matrix and identify what your responsibilities are. And see if you fulfill those responsibilities. Also, we are going to do a quick verification to see that based on the implementation does it actually make sense – the shared responsibility matrix? Service providers say they are going to be responsible for those services does it actually make sense? We’re going to take a look at that as well.
KLC evaluates the adequacy of documentation
[Paul] okay Kyle do either the Gap Assessment, the CMMC Gap Assessment or the CMMC Readiness Assessment, do those include an evaluation of the adequacy of the supporting documentation? Documentation that clients need to be able to demonstrate that they’re in compliance with a particular practice.
[Kyle] yes yep absolutely. So, we will look at all the supporting documents the meaning policies procedures any of the SOPs that’s you know, standard operating procedures. Whatever document that you have. Acceptable use policy, incident response plan, whatever plan, the policies, procedures that you have. We will be able to review. We’ll see if they are sufficient. And if there are any gaps, we’ll identify them.
Gap Assessment client deliverable package
[Paul] okay good what does the deliverable package look like? What should a client be expecting with that?
[Kyle] yeah, the deliverables. We’ll give you the system security plan at the high level. An understanding where you are right now. We’re going to give you a POAM, the gaps, and we’re going to help you identify the priority. Give you the roadmap for how you should approach remediating these gaps right. We’ll give you the priority based on the risk as well as the effort. So low risk low effort first right. Because then you can get rid of a lot of the easy tasks what’s your score? And we will give you the SPRS score that you are going to submit based on the DFARS 252.204-7020 right. You are required to submit a score to SPRS. So, we will give you that score. And if you have any questions about submitting the SPRS we’ll help you. But this eventually is our deliverable for our Gap Assessment service.
KLC Consulting is a cleared C3PAO candidate firm
[Paul] okay good okay. So, Kyle to wrap it up, KLC Consulting – we are a cleared candidate C3PAO firm. We have Provisional Assessors and Provisional Instructors, soon to be. This is our niche specialty: Providing compliance solutions for NIST 800-171 and CMMC. In fact, we specialize in providing the most affordable solutions that are available today. So, if you have any questions about Gap Assessments or Readiness Assessments. Or any questions at all about CMMC and NIST 800-171, I highly encourage that you contact us. We’ll have our contact us page link at the end of this video and we look forward to hearing from you! Thank you very much Kyle!
[Kyle] Thank you for checking out our CMMC Readiness Assessment Video!
Check out our CMMC Consulting Service Page for the most affordable NIST 800-171 and CMMC compliance consulting service options available today!
Do I need a CMMC Gap Assessment or a Readiness Mock Assessment
Understanding where you are in your compliance journey determines which engagement you need:
| Feature / Objective | CMMC Gap Assessment | CMMC Readiness Mock Assessment |
| Primary Goal | Identify missing controls, map CUI, and build a POA&M roadmap. | Simulate formal assessment conditions to verify audit readiness. |
| Current Posture | Actively implementing NIST SP 800-171 or updating an unvalidated score. | All 110 requirements are implemented and fully supported by evidence. |
| CUI Data Flow | Uncertain or unverified across non-IT departments. | Fully documented, scoped, and validated. |
| Deliverable Focus | Prioritized remediation roadmap, CUI flow map, and recommended SPRS score. | Final pass/fail readiness determination before engaging an auditor. |
| Core Question | “Where are our gaps, and what should we fix first?” | “Are we ready to pass an official C3PAO assessment today?” |
Frequently Asked Questions
Do we still need a CMMC Gap Assessment during the Phase II pause?
Yes. C3PAO Level 2 certification requirements are suspended, but DFARS 252.204-7012 has mandated NIST SP 800-171 since December of 2017. DFARS 252.204-7019 and -7020 require an active CMMC self-assessment score in SPRS, which contracting officers evaluate prior to awarding contracts.
How does working with a C3PAO help our CMMC self-assessment?
While a CMMC Gap Assessment is advisory, having an authorized C3PAO evaluate your environment adds significant third-party credibility. Prime contractors frequently discount internal DIY assessments, whereas a C3PAO-backed assessment gives prime customers confidence in your supply chain security.
How long does a CMMC Gap Assessment take?
A standard engagement for small to midsize contractors typically takes two to four calendar weeks, depending on system complexity, facility count, and MSP responsiveness.
Establish a Defensible NIST SP 800-171 Baseline Today
Whatever emerges from the Department of War’s CMMC review, your immediate requirements are clear: know where your CUI flows, ensure NIST SP 800-171 is implemented, and verify that your SPRS score is fully defensible.
"*" indicates required fields
Psssst. We’re cybersecurity professionals and dedicated privacy advocates. Rest assured, the confidentiality of your information is our top priority!