
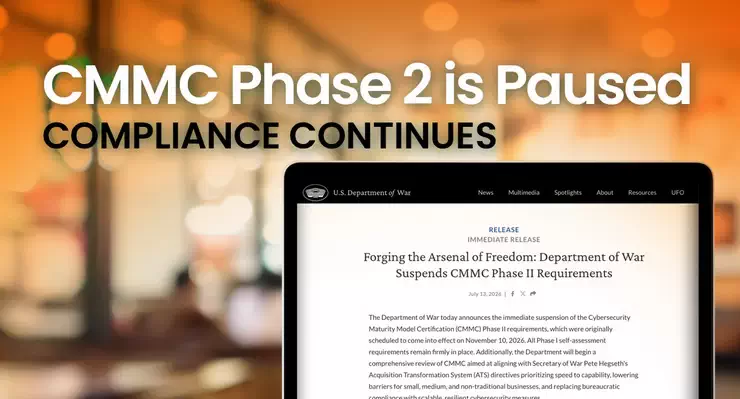
As many of you are aware, the Department of War (DoW) recently issued a memorandum suspending the transition to CMMC Phase 2 requirements, which were originally scheduled to take effect on November 10, 2026. The DoW CIO will initiate a 60-day review of the program under a newly established CMMC Reform Task Force.
In times of regulatory adjustment, immediate reaction often breeds impulsive reaction. But we want to provide you with steady, actionable guidance on what this pause actually means for your organization, how prime contractors are responding, and how the official CMMC Ecosystem is proceeding.
9.2.26
CMMC Newsflash: DIBCAC Actively Auditing Level 2 Self-Assessments
According to KLC Consulting President and CISO Kyle Lai, our team has identified a critical trend across the Defense Industrial Base (DIB). Over the past several months, the Defense Industrial Base Cybersecurity Assessment Center (DIBCAC) contacted five defense contractors to conduct government-led assessments after each company self-attested to a 110 score in SPRS. Each organization immediately engaged KLC Consulting for an official CMMC Level 2 certification assessment. In every instance, DIBCAC deferred its government assessment upon receipt of an executed C3PAO engagement letter.
This reflects a broader ecosystem pattern: DIBCAC is actively reviewing SPRS submissions to verify self-attested implementation. Contractors handling Controlled Unclassified Information (CUI) under DFARS 252.204-7012 face heightened scrutiny, making self-assessment accuracy an urgent operational priority.
If your organization relies on a self-assessment, inaction introduces unnecessary risk. Depending on your current posture, two clear paths establish verified compliance:
- Option 1: Execute a C3PAO Level 2 Certification Assessment (Active DIBCAC Inquiries). For contractors facing government review, producing an executed C3PAO engagement letter—confirming a bound assessment scope, established target dates, and a commitment to submit final findings – allows your organization to complete the assessment through an accredited C3PAO rather than a direct government audit.
- Option 2: Commission a C3PAO Mock Assessment (Proactive Validation). For organizations not yet contacted, a mock assessment provides objective verification of your SPRS score before DIBCAC initiates review. An independent evaluation uncovers remediable gaps early and provides defensible evidence supporting your compliance posture.
Whether your organization requires immediate third-party certification or proactive validation, engaging an accredited C3PAO replaces regulatory uncertainty with verifiable confidence across the defense marketplace.
Note: To support your preparation, KLC Consulting provides a preferred, discounted rate on mock assessments bundled with an official CMMC Level 2 Certification Assessment.
July 30, 2026
CMMC Phase 2 Suspension Update from Kyle Lai continues here
Consult Your Primes and Customers First
During this 60-day review period, the most constructive action your organization can take is to proactively contact your prime contractors or direct Department of War customers to clarify their specific security expectations.
Early indications and market feedback suggest that prime contractors are choosing to stay the course. Because Primes remain legally responsible for their supply chains, their operational default is to maintain momentum on existing compliance requirements. They are largely continuing to expect robust, verifiable cybersecurity postures from their subcontractors, regardless of the temporary pause in the Department’s formal Phase 2 rollout schedule. Engaging in these collaborative conversations early will ensure your business remains aligned with their risk tolerance and pipeline requirements.
Does the CMMC pause give us more time to complete our POA&M?
A: Not automatically. The suspension affects the rollout of mandatory Phase II C3PAO requirements, not the underlying obligation to protect CUI and accurately report your implementation of NIST SP 800-171.
Your required remediation timeline depends on the contract terms, the type of assessment, and whether the POA&M is connected to a formal CMMC conditional status. Organizations should continue addressing known deficiencies and ensure that their SSP, POA&M, and SPRS score accurately reflect the current state of their environment. Phase I self-assessment requirements remain in place.
We are midway through an assessment or consulting engagement. Should we stop work during the review?
A: Stopping automatically may create more cost and disruption later. The Phase II suspension changed how compliance may be independently verified, but it didn’t remove the security requirements already included in applicable defense contracts.
DFARS 252.204-7012 continues to require adequate security and implementation of NIST SP 800-171 for covered contractor information systems. Contracting officers also continue to verify that applicable contractors have a current NIST SP 800-171 assessment score in SPRS before award, option exercise, or contract extension.
Review the purpose of your current engagement before deciding. Remediation, CUI scoping, SSP development, evidence collection, and SPRS validation may still be necessary even when an immediate certification assessment is no longer required.
Can we pause our cybersecurity compliance spending?
A: The Phase II suspension isn’t a suspension of the underlying requirement to protect CUI.
The Department has stated that Phase I self-assessment requirements remain in place and that NIST SP 800-171 Rev. 2 compliance will continue to be evaluated through self-assessments and selected government-led assessments.
Applicable contractors still need to:
- protect covered defense information under DFARS 252.204-7012;
- maintain an accurate and current NIST SP 800-171 assessment in SPRS where required;
- keep their SSP, POA&M, scope, and reported score aligned with their actual environment.
Pausing unnecessary certification spending may be reasonable for some organizations. Pausing security implementation, remediation, documentation, or accurate self-assessment is a different decision and may create contract, operational, and cybersecurity risk.
Use the review period to complete known remediation, verify your CUI scope, update your SSP and POA&M, and ensure your SPRS submission remains defensible.
Key Takeaways from The Cyber AB Statement
On July 15, 2026, The Cyber AB released an official statement addressing the suspension. The accreditation body emphasized that while Phase 2 implementation milestones are temporarily paused, the core operational machinery of the CMMC program remains fully active and available.
- Assessments and Systems Remain Operational: Independent C3PAO Level 2 certification assessments are not halting. The eMASS and SPRS systems remain fully operational to process and record assessment activity. CMMC Level 2 Certificates remain valid for 3 years.
- DFARS and NIST Compliance is Unchanged: Standard NIST SP 800-171 and DFARS 252.204-7012 requirements remain in place and fully enforceable. Contractors are still legally obligated to protect Controlled Unclassified Information (CUI).
- Mitigating False Claims Act Risk: Independent validation can strengthen the factual basis supporting management affirmations and help identify discrepancies before they affect an SPRS submission or government-led review.
- Training and Professional Credentials Move Forward: CAICO-sanctioned training, professional examinations (such as CCA and CCP certifications), and Registered Practitioner services continue without interruption.
Summary of the Current Regulatory Landscape

The Path Forward with KLC Consulting
Compliance with foundational cybersecurity requirements is not going away; rather, the Department is seeking the right balance of security and efficiency.
We will continue to monitor the task force’s progress and provide clear, objective updates. If you have questions regarding how this pause impacts your active preparation, your current SSP, or your upcoming assessment plans, please reach out to us directly.
In addition to continuing to provide CMMC Level 2 Certification Assessments, KLC Consulting can help your company scope your CUI, conduct a Gap Assessment, prepare your self-assessment SPRS submission, and support the imminent transition from NIST 800-171 Revision 2 to Revision 3.
"*" indicates required fields
Psssst. We’re cybersecurity professionals and dedicated privacy advocates. Rest assured, the confidentiality of your information is our top priority!
Additional Resources
- DoW Memo July 13, 2026: https://dowcio.war.gov/Portals/0/Documents/Library/CMMC-ReformMemo.pdf.
- CyberAB Statement July 15, 2026: https://cyberab.org/News-Events/Press-Releases/statement-on-the-department-of-wars-suspension-of-cmmc-phase-ii-requirements.
- The Cyber AB will host a national Town Hall on Tuesday, July 28, 2026, at 6:00 PM EDT to address the Phase II pause and outline next steps. You can register directly on The Cyber AB website.
- Request For Information: Reforming CMMC and Reducing Compliance Burden for the Defense Industrial Base (DIB). Your active participation in this RFI is highly encouraged. Please note submissions are due by August 14, 2026 12:00 PM EDT.

Stay up to date with our CMMC News Flash
"*" indicates required fields