
What does the Department of War’s recent decision to pause CMMC Phase 2 rollout actually mean for defense contractors? In this video, Kyle Lai, President and CISO at KLC Consulting, breaks down the key changes, expectations, and critical steps Defense Industrial Base (DIB) organizations must take during this temporary suspension.
Key Highlights Covered in the Video:
- What Changed (and What Didn’t): While mandatory third-party C3PAO certifications for Phase 2 are paused during a 60-day study by the CMMC Reform Task Force, foundational requirements like DFARS 252.204-7012 and NIST SP 800-171 remain strictly in effect.
- Audit Risks & Self-Assessments: DIBCAC will continue conducting audits. Learn why you must retain documentation, artifacts, and evidence for six years to prepare for potential DIBCAC reviews or Department of Justice (DOJ) False Claims Act scrutiny.
- Shift in Accountability: Discover why self-assessment places direct legal and personal accountability on your organization’s Affirming Official to attest to control compliance and accuracy in SPRS.
- Prime Contractor Expectations: Why staying on top of your prime contractors’ expectations, and maintaining high assessment standards can help you stand out from your competitors.
CMMC Phase 2 Suspension Update transcript
Hi, my name is Kyle Lai, president and CISO at KLC Consulting. Today, I want to talk about the DoD announcements of the pause of CMMC Phase Two.
We’re going to talk about what’s changed and what’s not changed, the prime contractors’ expectation, and also what CMMC is going to look like after the task force completes their study.
So DoW made an announcement on July 13th that will pause all the CMMC phase two rollout. That means there is no longer a requirement for third party certification assessments.
The DoD is launching a 60-day study on the CMMC program by the CMMC Reform Task Force. The DoD still requires DIB organizations to meet the DFARS 252.204-7012 and the NIST 800.171 Rev 2 requirements.
DIBCAC, which is a DOD audit organization, will still conduct audits on the DIB organizations.
When you are doing a self-assessment, you still need to keep all the artifacts, the documentation, screenshots, or policies, procedures, network diagrams. You still need to zip them up, archive it, put it away for six years, just in case the DIBCAC organization wants to audit.
The responsibility and accountability for a DIB organization when performing a self-assessment versus having a third-party C3PAO certification assessment. When you are doing a self-assessment, you still need to go through all 110 requirements and the 320 assessment objectives.
If you have any deficiencies, you still need to put yourself into conditional status for the self-assessment. Meaning, that you have deficiencies that are allowed under CMMC. You still need to address these deficiencies within 180 days, according to the self-assessment.
If you compare the two, the only difference that I want to point out is the shift of the responsibilities. If you are using a C3PAO to conduct the assessment, that means the C3PAO is responsible for attesting the validity, accuracy, and sufficiency, the effectiveness of the controls that you implemented.
The C3PAO is the one entering the results into the emails which transfer to the SPRS system. Now if you are doing the self-assessment, that means you the DIB organization, you are responsible for entering the score into your SPRS system.
The affirming official within the DIB organization is going to be the one personally accountable, responsible for the accuracy, the validity, effectiveness, and the compliance of all these requirements.
If you claim to have a score of 110, the perfect score, and the results are lower than 110, then they will hold the affirming official accountable.
According to the Cyber AB, which is the CMMC accreditation body, press release, the certificate continues to be valid for three years. And all these systems that are supporting the C3PAOs are still up and running. For example, the eMASS and the SPRS systems.
Right now, the task force has been tasked to reduce the burden for implementing the NIST 800-171 and also still make it effective because what we have seen on the DFARS 252.204-7012, in 2017 when it was released, all the defense contractors, they needed to check the box saying, I comply and meet the requirements of NIST 800-171. Everybody checked that box.
But, the DOD inspector general came in to look at the actual progress. So what they actually saw is that 80% of the companies either never heard of DFARS 7012 requirements, they checked the box, and don’t even know it’s been checked. So at the end, 80% of the companies, they said, I comply. They were not in compliance.
If you are not in compliance, then you are at the risk of possibly getting audited. Or saying that you are complying with a score of 110, but you are not, then you will have a risk of false claim act against you; that will be handled by the Department of Justice.
Yeah, so you want to still keep going, comply and meet the requirements because if you are handling CUI today, store, process or transmit CUI, look at the contracts that you have. Most likely you already have the requirement to meet the DFARS 252.204-7012. And if you already checked that box, you want to make sure that you are doing what you said you are doing.
Talk to your prime contractors because you need to understand what their expectations are for the self-assessment, what is their expectation today, and what’s their expectation in the future.
Prime contractors are keeping a list of companies going through the independent third-party validation by a C3PAO. So you want to check with your prime contractors and see if they need to get an update of your status.
Whether you want to proceed with an independent assessment to stand out from your competitors, scale back your scope, or need help with your self-assessment, our team is here for you. Reach out to us today to start the conversation.
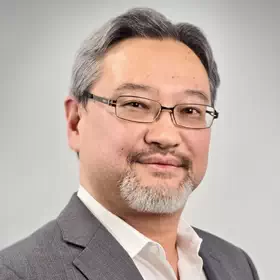
Kyle Lai
President and CISO
Lead CMMC Certified Assessor (CCA)
Certified CMMC Professional (CCP)
Provisional Instructor (PI)
CISSP, CSSLP, CISA, CDPSE, CIPP/US, CIPP/G, ISO 27001 Lead Auditor
Nationally recognized as a DoD cybersecurity expert with over 20 years of experience in cyber and I.T., Kyle assesses and architects NIST 800-171 and CMMC compliance solutions for U.S. Defense Industrial Base (DIB) companies. He consulted as a security advisor to several Fortune 500 companies and the DoD. Kyle now specializes in developing cost-effective CMMC compliance solutions for: Manufacturers, Aerospace, Engineering, Software Development, and MSP/IT companies.
Kyle’s distinguished career includes consulting for high-profile clients like ExxonMobil, Zoom, DISA, Boeing, HP, Fidelity Investments, Microsoft, Akamai, and PwC. He served as the former CISO to Pactera (a Blackstone Portfolio Co.) and Brandeis University – Heller School. Kyle was also an operations manager for DISA Cybersecurity Portal (predecessor of public.cyber.mil – a department within the U.S. Department of Defense).
His broad cybersecurity expertise spans security strategy, policies, program management, vulnerability management, penetration testing, incident response, business continuity, regulatory compliance, application security, and third-party risk management. (continues)
About KLC Consulting
KLC Consulting is an Authorized C3PAO specializing in CMMC assessments and NIST 800-171 compliance for the Defense Industrial Base (DIB). Our team of Cyber AB-authorized Lead CMMC Certified Assessors has a combined 75 years of experience in the cybersecurity field, allowing us to deliver objective, high-quality CMMC Level 2 assessments and readiness services for organizations from Fortune 500s to small subcontractors. Read more about us here.