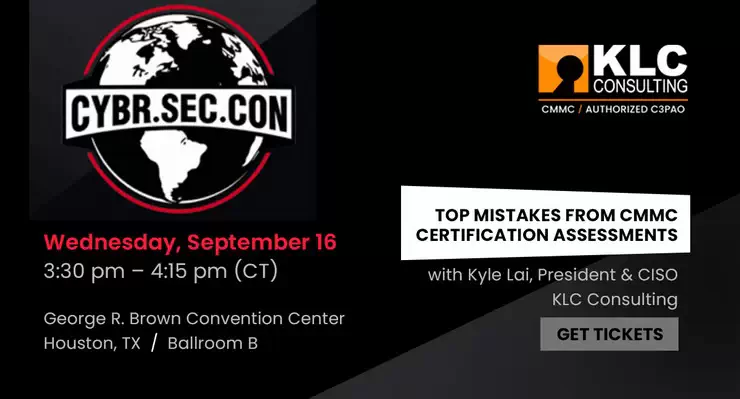

Wednesday, September 16, 2026
3:30 pm – 4:15 pm ET
Houston, TX
SPEAKER: Kyle Lai, President & CISO, KLC Consulting
For defense contractors navigating the Department of Defense (DoD) supply chain, understanding the Cybersecurity Maturity Model Certification (CMMC) requirements can be a daunting task. Achieving compliance is a strict requirement to win and keep DoD contracts, making the stakes incredibly high. However, many companies going through CMMC for the first time fail their formal third-party assessment preparation due to simple, avoidable mistakes.
This presentation is designed specifically for organizations approaching their very first CMMC compliance hurdle. Led by authorized CMMC 3rd Party Assessment Organization (C3PAO) and Lead CMMC Certified Assessor (LCCA), this session strips away the complex jargon to explain exactly how an official review works from start to finish. We will dive directly into the most common pitfalls faced by companies going through the process for the first time, such as failing to properly scope where sensitive government data lives, confusing “written policies” with actual technical implementation, and mismanaging the security of modern tools like custom software and AI. Attendees will leave with a clear roadmap of what to expect and the practical steps needed to pass their first assessment with confidence.
3 Key Takeaways for the Audience
- Demystify the Assessment Process: Learn exactly what happens during an official C3PAO assessment timeline so your team is fully prepared for interview week.
- Avoid First-Time Pitfalls: Recognize the most common errors related to scope boundaries and documentation before they affect your certification.
- Gather the Right Evidence: Understand how to properly organize your policies and technical artifacts to prove your security controls are actively working.
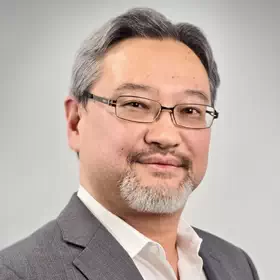
Kyle Lai
President and CISO
Lead CMMC Certified Assessor (CCA)
Certified CMMC Professional (CCP)
Provisional Instructor (PI)
CISSP, CSSLP, CISA, CDPSE, CIPP/US, CIPP/G, ISO 27001 Lead Auditor
Nationally recognized as a DoD cybersecurity expert with over 20 years of experience in cyber and I.T., Kyle assesses and architects NIST 800-171 and CMMC compliance solutions for U.S. Defense Industrial Base (DIB) companies. He consulted as a security advisor to several Fortune 500 companies and the DoD. Kyle now specializes in developing cost-effective CMMC compliance solutions for: Manufacturers, Aerospace, Engineering, Software Development, and MSP/IT companies.
Kyle’s distinguished career includes consulting for high-profile clients like ExxonMobil, Zoom, DISA, Boeing, HP, Fidelity Investments, Microsoft, Akamai, and PwC. He served as the former CISO to Pactera (a Blackstone Portfolio Co.) and Brandeis University – Heller School. Kyle was also an operations manager for DISA Cybersecurity Portal (predecessor of public.cyber.mil – a department within the U.S. Department of Defense).
His broad cybersecurity expertise spans security strategy, policies, program management, vulnerability management, penetration testing, incident response, business continuity, regulatory compliance, application security, and third-party risk management. (continues)
About KLC Consulting
KLC Consulting is an Authorized C3PAO specializing in CMMC assessments and NIST 800-171 compliance for the Defense Industrial Base (DIB). Our team of Cyber AB-authorized Lead CMMC Certified Assessors has a combined 75 years of experience in the cybersecurity field, allowing us to deliver objective, high-quality CMMC Level 2 assessments and readiness services for organizations from Fortune 500s to small subcontractors. Read more about us here.