
CMMC Assessment and Independent Validation for Defense Contractors
Experienced Assessors. A Collaborative, Human Approach.
KLC Consulting is an authorized C3PAO providing CMMC Level 2 Certification Assessments and independent readiness validation for defense contractors. Our assessors bring proven practical cybersecurity experience to every engagement and approach each organization with professionalism, fairness, and respect.
Move Forward with Clarity During the CMMC Review
The Department of War’s Phase II suspension changed the timetable for mandatory third-party assessments. It did not remove the underlying responsibility to safeguard Controlled Unclassified Information or meet applicable NIST SP 800-171 requirements.
Organizations should begin by speaking with their prime contractors and government customers to understand what their current contracts, solicitations, and supplier requirements demand. Some contractors may still benefit from completing a CMMC Level 2 Certification Assessment, while others may need an independent readiness review or a different compliance path.
KLC Consulting can help you understand the available assessment options and determine which engagement fits your current business requirements.
What the July 13th Department of War’s CMMC Phase 2 Pause Means for you.
The CMMC Level 2 Certification Assessment Process
When a CMMC Level 2 Certification Assessment is required or voluntarily pursued, the official process generally follows four stages.
Phase 1
Planning & Scope
Confirm assessment readiness, define the CUI environment, and establish the assessment scope.
Phase 2
Assessment
Conduct the assessment using Examine, Interview, and Test methods.
Phase 3
Results & Reporting
Receive the assessment results and final or conditional CMMC status.
Phase 4
Conditional Status & Closeout
If eligible deficiencies remain, complete the POA&M and closeout process within 180 days
NIST SP 800-171 Compliance is Still Required even if a Third-Party Certification is Voluntary
The CMMC Phase II suspension changed how compliance is verified, it did not eliminate a contractor’s underlying obligation to protect CUI.
Defense contractors with applicable DFARS 252.204-7012 requirements must continue implementing NIST SP 800-171 and maintaining an accurate, current assessment in SPRS. At this time, the suspended Phase II rollout means a C3PAO certification assessment is not universally required for those contractors.
A third-party assessment may still be valuable or requested when:
- a prime contractor or customer wants independent assurance;
- an active contract or solicitation still contains a certification requirement;
- leadership wants stronger evidence before affirming an SPRS score;
- the organization wants to complete certification voluntarily;
- preparation for a potential government-led assessment is important.
Flexibility Built Around a Changing Environment
Regulatory uncertainty should not force your organization into an inflexible engagement. KLC Consulting structures its assessment agreements to account for changes in your CUI environment, customer expectations, and applicable CMMC requirements.
Adaptive Scope and Pricing
Your assessment scope and price are based on the systems, locations, service providers, personnel, and CAGE codes included within your CUI environment. If that environment changes before the assessment begins, KLC Consulting will review the impact and adjust the engagement where appropriate.
Independent Validation
A CMMC Level 2 Certification Assessment provides formal third-party evaluation of your implementation of the applicable security requirements. Even when certification is not immediately mandated, independent validation may provide additional assurance to company leadership, prime contractors, customers, and other stakeholders.
Engagement Flexibility
If government requirements materially change before your scheduled assessment begins, KLC Consulting will work with you to evaluate the appropriate next step. Depending on the circumstances and the terms of your agreement, that may include modifying the assessment scope, rescheduling the engagement, or moving to another eligible KLC Consulting service.
Why KLC Consulting? Professional Assessors, Not “Gotcha” Assessors
A Level 2 Certification Assessment must be rigorous, objective, and independent. It does not need to be adversarial.
KLC Consulting’s assessors take the time to understand your environment, examine the evidence you present, and evaluate how your security practices operate in the real world. We communicate clearly throughout the process and focus on making the assessment organized, transparent, and professionally managed.
Our role during a certification assessment is to determine whether the required practices are implemented and supported by sufficient evidence. We cannot provide remediation consulting to an organization we are certifying, but we can explain the assessment process, evidence expectations, findings, and available assessment outcomes.
Choose the Assessment Path That Fits Your Needs
CMMC Level 2 Certification Assessments
An official assessment conducted by an authorized C3PAO, with results submitted through the established CMMC process.
CMMC Level 2 Readiness “Mock” Assessments
An independent practice assessment that uses the same Examine, Interview, and Test methodology to identify met and unmet requirements without providing prohibited remediation consulting.
Mock Assessment and Certification Bundle
A discounted option for organizations that want an independent readiness review followed by an official certification assessment from KLC Consulting.
Organizations seeking a Gap Analysis with remediation recommendations should use KLC Consulting’s separate consulting path. Because that service includes guidance on correcting deficiencies, KLC Consulting cannot later serve as the independent C3PAO for the same certification scope.
Frequently Asked Questions About a C3PAO Assessment
Below are some of the most frequently asked questions we get regarding a C3PAO CMMC Assessment.
If you have any other questions, we’d love to hear them [Really!] Please contact us.
Since Phase II was suspended, do we still need to implement all 110 NIST SP 800-171 requirements?
A: Yes. The suspension affects the rollout of mandatory C3PAO assessments, not the underlying obligation to protect Controlled Unclassified Information.
During the suspension, CMMC Level 2 is being enforced through self-assessments and selected government-led assessments. Organizations subject to applicable DFARS requirements must still assess their implementation of all 110 NIST SP 800-171 Rev. 2 requirements, submit the results to SPRS, and complete the required annual affirmation.
What should we do if an active contract or solicitation still requires a Level 2 C3PAO assessment?
A: Contact your prime contractor or government contracting officer and request written clarification.
The Department has directed program managers to remove Level 2 C3PAO and Level 3 DIBCAC requirements from active solicitations through formal amendments as soon as practicable. Existing contracts containing those requirements are to be modified before the next option period or during the next scheduled administrative modification.
Until the solicitation is amended or the contract is formally modified, do not assume the existing language has disappeared. Confirm the current requirement in writing before changing your assessment plans.
How do you know when you are ready for an assessment?
A: Determining your readiness for a CMMC assessment involves a comprehensive evaluation of your organization’s cybersecurity posture. Here are some key indicators:
- Understanding of CMMC Requirements: You should have a thorough understanding of the specific CMMC requirements applicable to your organization’s size, industry, and data handling practices.
- Implementation of Security Controls: You should have implemented the necessary security controls to meet the CMMC requirements, including access control, incident response, and data protection measures.
- Documentation and Evidence: You should have the necessary documentation and evidence to demonstrate compliance with CMMC standards. This includes policies, procedures, and system configurations.
What happens if some requirements are not met?
Assessment outcomes depend on the number and type of unmet requirements. Some eligible findings may result in conditional status and a defined POA&M closeout period. Other findings may prevent certification until they are corrected and reassessed. KLC Consulting documents the findings and explains the applicable assessment outcome while maintaining the independence required of a C3PAO.
Can you do an assessment remotely?
A: Yes, many C3PAOs offer remote assessment services. Remote assessments can be conducted using virtual tools and technologies, reducing the need for on-site visits. However, some aspects of the assessment, such as physical infrastructure reviews, may require on-site presence.
How does a C3PAO determine if I pass?
A: C3PAOs use a rigorous evaluation process to determine if an organization passes a CMMC assessment. This process typically involves:
- Document Review: Examining relevant documentation, such as policies, procedures, and system configurations.
- Interviews: Conducting interviews with key personnel to gather information about your organization’s cybersecurity practices.
- Testing: Conducting tests and assessments to evaluate the effectiveness of your security controls.
Based on these evaluations, the C3PAO will assess your organization’s compliance with the CMMC requirements and determine whether you pass or fail.
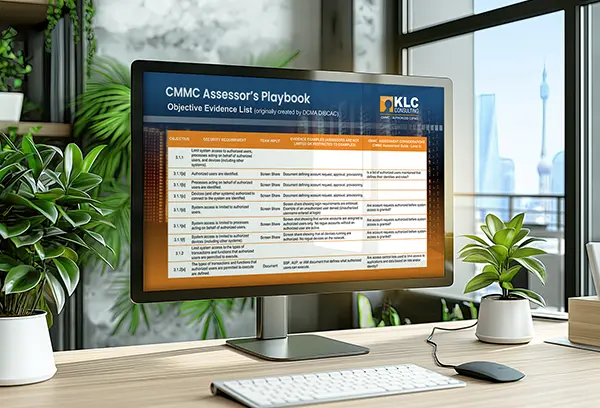
In addition to these methods, C3PAOs often rely on an objective evidence list to support their assessment. This list outlines the specific types of evidence required to demonstrate compliance with the CMMC requirements. This evidence can include:
- System configurations: Documentation of system settings and configurations.
- Security controls: Evidence of implemented security controls, such as access control measures, incident response plans, and data protection policies.
- Risk assessments: Documentation of risk assessments and mitigation strategies.
- Training records: Evidence of employee training on cybersecurity best practices.
By reviewing this objective evidence, C3PAOs can verify your organization’s compliance with the CMMC requirements and make an informed determination about your assessment status. Check out our assessors playbook to guide you.

The team’s professionalism, expertise, and attention to detail were evident throughout our CMMC certification process. They made what could have been an overwhelming experience remarkably smooth and clear. Highly recommend their services to anyone navigating CMMC certification!
– Marlene Andersch, CEO of rockITdata
CMMC Level 2: Mock + Assessment Bundle
Prepare with Confidence. Save up to 50% on Mock when bundled.
Prepare your organization for assessment with a comprehensive simulation of the official certification process. Our Lead CMMC Certified Assessors apply the same Examine, Interview, and Test methodology used in a formal assessment to identify met and unmet requirements, highlight evidence gaps, and provide a clear picture of your current readiness before certification.
The Bundle Advantage:
- Full Evaluation: We assess all 110 CMMC Level 2 security requirements across your defined assessment scope.
- Official Assessment Methodology: We apply the CMMC Assessment Process using Examine, Interview, and Test methods.
- Detailed Readiness Results: Receive a report identifying met and unmet requirements, along with a simulated assessment outcome.
- Experienced Assessment Team: Work with cybersecurity professionals bringing a combined 75 years of experience and a clear, respectful, professionally managed approach.
Detailed Readiness Results: Receive a report identifying met and unmet requirements, along with a simulated assessment outcome.
Key Insights and Preparing for Your CMMC Level 2 Assessment
This video was recorded before the July 2026 Phase II suspension. The assessment mechanics remain useful, but references to rollout deadlines and mandatory certification should be understood in that earlier context.
While regulatory enforcement timelines and mandatory third-party audit schedules are evolving under the current framework pause, the technical core of data protection remains unchanged. In this briefing, Kyle Lai, President and CISO of KLC Consulting, breaks down the critical mechanics of Level 2 security requirements, common compliance pitfalls, and data isolation strategies.

The Value of Ongoing Independent Review
Cybersecurity environments change over time. New employees, software updates, system migrations, service providers, and scope changes can cause documentation and reported scores to drift away from actual implementation.
Periodic independent review can help identify changes in scope, evidence, configuration, and control operation before they affect the accuracy of an SPRS submission or management affirmation.
Why Partner with KLC Consulting for Ongoing Validation?
- Drift Detection & Cost Efficiency: Network environments change constantly as new employees join, software updates roll out, and hardware is replaced. Returning to KLC Consulting for periodic check-ins prevents compliance drift. Because we already know your architecture, we can validate your delta changes faster and at a fraction of the cost of a ground-up assessment.
- Operational Continuity: We maintain a historical record of your compliance trajectory. When the CMMC Reform Task Force finalizes its updated framework, you won’t have to scramble or play catch-up; we will seamlessly pivot your existing baseline to meet the new milestones.
- FCA Risk Mitigation: Our lead assessors act as an independent safety net. Before your corporate officers sign their names to annual federal performance portals, our mock validation gives your leadership team the technical data and confidence they need to attest accurately.
Conquer Your Assessment with Our Free Playbook
Demystify your CMMC Level 2 Assessment! Our free playbook simplifies the official “Objective Evidence List” from the DCMA DIBCAC. Get clear insights into C3PAO expectations for each security practice and what evidence they’ll require. Be fully prepared to ace your assessment.