
C3PAO Assessments for IT/Managed Service Providers
Now that the CMMC Program Rule (32 CFR Part 170) is effective, CMMC Level 2 Certification is a mandatory requirement for Defense Industrial Base (DIB) companies to win and retain DoD contracts involving Controlled Unclassified Information (CUI). For IT/Managed Service Providers (MSPs), this presents unique complexities. KLC Consulting, an authorized C3PAO, brings deep expertise in both CMMC assessments and the distinct technical and business models of IT/MSP operations, making us uniquely equipped to provide the comprehensive and effective assessment your organization needs to meet these critical DoD compliance requirements.
Avoiding CMMC Pitfalls Before an Assessment
- Shared Responsibility Matrix (SRM): To prevent assessment failure, you must clearly define whether you or your client owns each CMMC control.
- Precise CUI Scoping: Accurately identify and map where CUI resides to ensure your services and systems are correctly scoped.
- Documentation and Evidence: CMMC requires proof of practice, not just a policy. Be ready to produce on-demand evidence like logs and anti-malware configurations.
- Client Preparation: CMMC certification delays or failures can occur if clients are not prepared to provide the required documentation demonstrating their compliance.
- Managing Sub-Providers: Ensure any third-party tools or cloud services provider (CSP), and managed service providers (MSP) you use are also compliant with CMMC requirements.
CMMC Level 2 Certification Assessment Process
The CMMC Level 2 assessment for IT/MSPs starts with scoping and a readiness review to define responsibilities for Controlled Unclassified Information (CUI) between you and your clients. A key step is developing and validating your Shared Responsibility Matrix (SRM), which clearly outlines who is accountable for each CMMC control.
Once the readiness phase is complete and your SRM is validated, the formal assessment can start. Our process includes:
- Cross-Functional Engagement: We work with your IT, security, and client service teams.
- Comprehensive Scope Verification: We meticulously verify your CUI boundary, data flows, and all related systems, users, and third-party vendors.
- Client Environment Integration & Shared Controls Evaluation: We review CUI handling in client environments, including inherited controls and shared responsibilities.
- Hybrid & Multi-Tenant Expertise: We evaluate compliance across your on-premises systems, specialized cloud environments (like Azure GCC High), and multi-tenant architectures.
Secure Clients with CMMC Certification
We gather evidence for each CMMC control through documentation review, interviews, and live demonstrations. Achieving CMMC certification allows MSPs to pass on inherited controls to clients, streamlining their compliance. Clear communication and thorough documentation are vital for a successful outcome.
Your Best C3PAO for Assessing DIB Manufacturers

KLC Consulting stands as the premier C3PAO for DIB manufacturers seeking CMMC certification. Our comprehensive assessment approach is grounded in deep, practical understanding of both cybersecurity and the manufacturing sector.
This enables us to precisely evaluate how CUI is protected within your design, production, and supply chain management systems. Furthermore, our team’s background, including former DoD cybersecurity professionals and military veterans, provides invaluable insight into the defense industrial base’s distinct challenges.
Our CMMC Certified Assessors (CCAs) bring deep, practical experience in:
- Hands-On Technical Assessment Capability: KLC Consulting’s assessors possess a deep, hands-on technical background. We are not merely auditors; their experience includes configuring and implementing security solutions in real-world environments. This practical expertise directly translates to their assessment methodology, enabling them to thoroughly evaluate the technical controls in a manufacturing setting, ask precise questions about implementation details, and effectively verify the operational effectiveness of security measures during an assessment.
- Efficiency in the Assessment Process: Our in-depth industry knowledge and technical expertise directly translate to a more efficient and less disruptive assessment for your manufacturing operations. We are adept at quickly identifying critical systems, understanding complex manufacturing processes, and asking targeted, relevant questions. This efficiency minimizes the disruption to a manufacturer’s production schedule and streamlines the overall certification journey.
- Assessing Complex DIB Manufacturing & Supply Chains: KLC Consulting excels at assessing the intricate IT infrastructures and deep supply chain integration common to DIB manufacturers. We expertly evaluate compliance across hybrid IT/OT environments, thoroughly assess any reliance on external IT providers, and understand how CMMC requirements propagate through your entire supply chain.
KLC Consulting’s blend of hands-on technical assessment capabilities and specialized industry insight makes us uniquely equipped to conduct thorough and efficient CMMC Assessments for defense manufacturers, setting you firmly on the path to continued success.
The KLC Consulting Approach
We understand the apprehension that comes with high-stakes assessments, which is why our approach is professional and collaborative—never adversarial or based on “gotcha” tactics. What truly sets us apart is our proven years of cybersecurity experience and a fair, insightful approach that understands the unique challenges of manufacturing environments. As an objective C3PAO, we are dedicated to validating your demonstrated security practices with clear understanding and a human touch, focusing on complete and accurate compliance confirmation.

Unsure About Your CMMC Readiness?
Many defense software companies grapple with CMMC Level 2 readiness. To alleviate this, KLC Consulting offers a Mock “Readiness” Assessment. This simulated evaluation mirrors the official CMMC assessment process, providing a realistic “practice run” to identify deficiencies and outline a clear remediation roadmap, so you undertake your formal assessment with confidence.
Save 50% on Your CMMC Readiness Bundle
To support the Defense Industrial Base, we offer a 50% discount on the Mock Assessment when it is bundled with your official CMMC Level 2 Certification Assessment. This package ensures you have a proactive, expert-led path to compliance while significantly reducing your overall certification costs. Contact us to lock in this bundle pricing.
Don’t Let Your Security Posture Drift
The Phase II suspension changed the third-party assessment timeline, not the underlying obligation to protect CUI. Use this period to verify your scope, close known gaps, align documentation with implementation, and ensure your SPRS submission accurately reflects your environment.
Conquer Your Assessment with Our Free Playbook
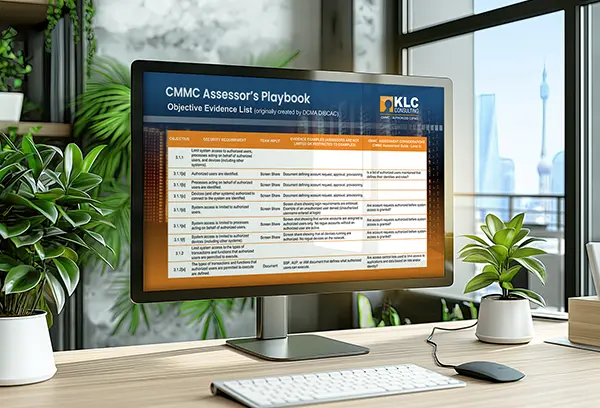
Demystify your CMMC Level 2 Assessment! Our free playbook simplifies the official “Objective Evidence List” from the DCMA DIBCAC. Get clear insights into C3PAO expectations for each security practice and what evidence they’ll require. Be fully prepared to ace your assessment.